Sunday, October 27, 2013

Controlling Bandwidth on an ASA: Traffic Policing and Shaping

You can leverage two ASA features to control or limit the amount of bandwidth used by specific traffic flows:

* Traffic policing

* Traffic shaping

With either method, the ASA measures the bandwidth used by traffic that is classified by a service policy and then attempts to hold the traffic within a configured rate limit. However, each method accomplishes the bandwidth control in a different manner.

With traffic policing, the packets are forwarded normally as long as the bandwidth threshold is not exceeded. However, packets that do exceed the bandwidth threshold are simply dropped.

In contrast, traffic shaping takes a more preemptive approach. Traffic is buffered before it is forwarded so that the traffic rate can be shaped or held within the threshold limit. The idea is to pull packets from the buffer at a rate that is less than the threshold so that no packets are dropped.

To use ASDM to configure traffic policing, begin by navigating to Configuration > Firewall > Service Policy Rules and adding a new service policy rule or editing an existing one. Define a matching condition that will classify the traffic that will be policed. Next, click the QoS tab in the Rule Action dialog box. Check the Enable Policing check box, and then choose either Input Policing or Output policing.


Use the police command as the action to send the matched traffic into a traffic policer.

ciscoasa(config)# access-list OUTBOUND_HTTP extended permit tcp any eq http any
ciscoasa(config)# class-map CLASS_HTTP
ciscoasa(config-cmap)# match ?

mpf-class-map mode commands/options:
  access-list                 Match an Access List
  any                         Match any packet
  default-inspection-traffic  Match default inspection traffic:
                              ctiqbe----tcp--2748      dns-------udp--53
                              ftp-------tcp--21        gtp-------udp--2123,3386
                              h323-h225-tcp--1720      h323-ras--udp--1718-1719
                              http------tcp--80        icmp------icmp
                              ils-------tcp--389       ip-options-----rsvp
                              mgcp------udp--2427,2727 netbios---udp--137-138
                              radius-acct----udp--1646 rpc-------udp--111
                              rsh-------tcp--514       rtsp------tcp--554
                              sip-------tcp--5060      sip-------udp--5060
                              skinny----tcp--2000      smtp------tcp--25
                              sqlnet----tcp--1521      tftp------udp--69
                              waas------tcp--1-65535   xdmcp-----udp--177
  dscp                        Match IP DSCP (DiffServ CodePoints)
  flow                        Flow based Policy
  port                        Match TCP/UDP port(s)
  precedence                  Match IP precedence
  rtp                         Match RTP port numbers
  tunnel-group                Match a Tunnel Group
ciscoasa(config-cmap)# match access-list ?

mpf-class-map mode commands/options:
  WORD  Access List name
ciscoasa(config-cmap)# match access-list OUTBOUND_HTTP
ciscoasa(config-cmap)# exit
ciscoasa(config)# policy-map MY_POLICY
ciscoasa(config-pmap)# ?

MPF policy-map configuration commands
  class        Policy criteria
  description  Specify policy-map description
  exit         Exit from MPF policy-map configuration mode
  help         Help for MPF policy-map configuration commands
  no           Negate or set default values of a command
  rename       Rename this policy-map
  <cr>
ciscoasa(config-pmap)# class CLASS_HTTP
ciscoasa(config-pmap-c)# ?

MPF policy-map class configuration commands:
  exit             Exit from MPF class action configuration mode
  help             Help for MPF policy-map class/match submode commands
  no               Negate or set default values of a command
  police           Rate limit traffic for this class
  priority         Strict scheduling priority for this class
  quit             Exit from MPF class action configuration mode
  service-policy   Configure QoS Service Policy
  set              Set connection values
  shape            Traffic Shaping
  user-statistics  configure user statistics for identity firewall
  <cr>
  csc              Content Security and Control service module
  flow-export      Configure filters for NetFlow events
  inspect          Protocol inspection services
  ips              Intrusion prevention services
ciscoasa(config-pmap-c)# police ?

mpf-policy-map-class mode commands/options:
  input   Police traffic in input direction
  output  Police traffic in output direction
ciscoasa(config-pmap-c)# police output ?

mpf-policy-map-class mode commands/options:
  <8000-2000000000>  Bits per second
ciscoasa(config-pmap-c)# police output 1000000 ?

mpf-policy-map-class mode commands/options:
  <1000-512000000>  Burst bytes
  conform-action    action when rate is less than conform burst
  <cr>
ciscoasa(config-pmap-c)# police output 1000000 conform-action ?

mpf-policy-map-class mode commands/options:
  drop           drop packet
  exceed-action  action when rate is within conform and conform + exceed burst
  transmit       transmit packet
  <cr>
ciscoasa(config-pmap-c)# police output 1000000 conform-action transmit ?

mpf-policy-map-class mode commands/options:
  exceed-action  action when rate is within conform and conform + exceed burst
  <cr>
ciscoasa(config-pmap-c)# police output 1000000 conform-action transmit exceed-action ?

mpf-policy-map-class mode commands/options:
  drop      drop packet
  transmit  transmit packet
  <cr>
ciscoasa(config-pmap-c)# police output 1000000 conform-action transmit exceed-action drop
ciscoasa(config-pmap-c)# exit
ciscoasa(config-pmap)# exit
ciscoasa(config)# service-policy MY_POLICY ?

configure mode commands/options:
  global     Enter this keyword to specify a global policy
  interface  Enter this keyword to specify an interface policy
ciscoasa(config)# service-policy MY_POLICY interface ?

configure mode commands/options:
Current available interface(s):
  dmz      Name of interface GigabitEthernet1
  inside   Name of interface GigabitEthernet0
  outside  Name of interface GigabitEthernet2
ciscoasa(config)# service-policy MY_POLICY interface outside


To configure traffic shaping in ASDM, begin by adding a new service policy rule or edit an existing one. Traffic shaping doesn't shape specific matched traffic; it shapes the default traffic that isn't matched or classified by any other traffic class. Therefore, you have to use the class-default class map to match the traffic. This is done by selecting the Use Class-Default As the Traffic Class option in the Traffic Classification Criteria dialog box.


Next, click the QoS tab in the Rule Actions dialog box and check Enable Traffic Shaping as the policy action. If you choose any matching criteria other than class-default, the Enable Traffic Shaping option will not be shown.


You can use the shape command as the action to send the matched traffic into a traffic shaper. Traffic shaping can be applied only to the bulk amount of traffic passing through an interface. Therefore, the matching condition you enter into the policy map configuration is important. The only permissible command is class class-default, followed by the shape command action.

ciscoasa(config)# policy-map outside-policy
ciscoasa(config-pmap)# class ?

mpf-policy-map mode commands/options:
  WORD            class-map name
  class-default   System default class matching otherwise unclassified packets

configure mode commands/options:
  WORD < 41 char  class-map name
  type            Specifies the type of class-map
ciscoasa(config-pmap)# class class-default
ciscoasa(config-pmap-c)# ?

MPF policy-map class configuration commands:
  exit             Exit from MPF class action configuration mode
  help             Help for MPF policy-map class/match submode commands
  no               Negate or set default values of a command
  police           Rate limit traffic for this class
  priority         Strict scheduling priority for this class
  quit             Exit from MPF class action configuration mode
  service-policy   Configure QoS Service Policy
  set              Set connection values
  shape            Traffic Shaping
  user-statistics  configure user statistics for identity firewall
  <cr>
  csc              Content Security and Control service module
  flow-export      Configure filters for NetFlow events
  inspect          Protocol inspection services
  ips              Intrusion prevention services
ciscoasa(config-pmap-c)# shape ?

mpf-policy-map-class mode commands/options:
  average  configure token bucket: CIR (bps) [Bc (bits)], send out Bc only per
           interval
ciscoasa(config-pmap-c)# shape average ?

mpf-policy-map-class mode commands/options:
  <64000-154400000>  Target Bit Rate (bits per second), the value needs to be
                     multiple of 8000
ciscoasa(config-pmap-c)# shape average 100000000
ciscoasa(config-pmap-c)# exit
ciscoasa(config-pmap)# exit
ciscoasa(config)# service-policy ?

configure mode commands/options:
Available policy-maps:
  outside-policy
ciscoasa(config)# service-policy outside-policy interface ?

configure mode commands/options:
Current available interface(s):
  dmz      Name of interface GigabitEthernet1
  inside   Name of interface GigabitEthernet0
  outside  Name of interface GigabitEthernet2
ciscoasa(config)# service-policy outside-policy interface outside

Saturday, October 19, 2013

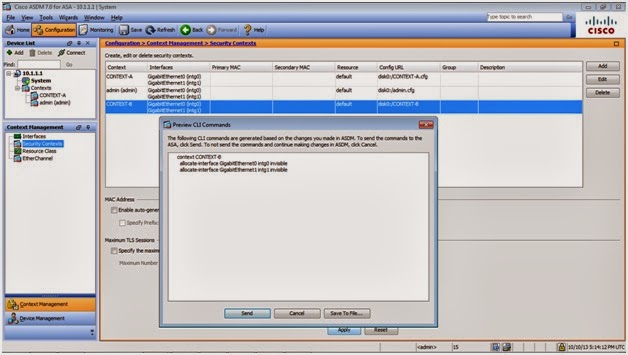
Configuring Virtual Firewall on an ASA

Limitations

Here are some important limitations regarding virtual firewalls on a Cisco ASA:

* Key features that are unsupported on a Cisco ASA in multiple mode are dynamic routing protocols, IPsec and SSL VPNs, multicast IP routing, threat detection, and Phone Proxy.

* The Cisco ASA 5505 does not support multiple mode. (This personally frustrates me).

* The number of Security Contexts you can create depends on the software licenses and the Cisco ASA hardware model used.

I had a discussion with our core design engineer and he mentioned that we should be able to run IPsec site-to-site VPNs on context-based firewalls. And sure enough after doing some research, Cisco has finally released a code to support this feature.

As of ASA code 9.0+, there's been an enhancement to support some of these features especially on Multi-Context VPN. Refer to useful links:

http://sevenlayers.wordpress.com/2012/09/13/cisco-multi-conext-vpn-is-finally-here-in-asa-release-9-0-a-few-years-too-late/

http://www.cisco.com/c/en/us/products/collateral/security/adaptive-security-appliance-asa-software/data_sheet_c78-714849.html


Configuration Tasks

Here is an overview for the configuration of virtual firewalls on the Cisco ASA.

Step 1: Enable multiple mode on the Cisco ASA.

Step 2: Create a Security Context.

Step 3: Allocate interfaces to the context.

Step 4: Specify the startup configuration location for the context.

Step 5: Configure the Security Context resource management.

Step 6: Configure each Security Context as a separate security appliance.


Licensed features for this platform:

Maximum Physical Interfaces       : Unlimited      perpetual
Maximum VLANs                     : 100            perpetual
Inside Hosts                      : Unlimited      perpetual
Failover                          : Active/Active  perpetual
VPN-DES                           : Enabled        perpetual
VPN-3DES-AES                      : Enabled        perpetual
Security Contexts                 : 2              perpetual    // EXCLUDES SYSTEM AND ADMIN CONTEXT
GTP/GPRS                          : Disabled       perpetual
AnyConnect Premium Peers          : 5000           perpetual
AnyConnect Essentials             : Disabled       perpetual
Other VPN Peers                   : 5000           perpetual
Total VPN Peers                   : 0              perpetual
Shared License                    : Disabled       perpetual
AnyConnect for Mobile             : Disabled       perpetual
AnyConnect for Cisco VPN Phone    : Disabled       perpetual
Advanced Endpoint Assessment      : Disabled       perpetual
UC Phone Proxy Sessions           : 2              perpetual
Total UC Proxy Sessions           : 2              perpetual
Botnet Traffic Filter             : Disabled       perpetual
Intercompany Media Engine         : Disabled       perpetual

This platform has an ASA 5520 VPN Plus license.

ciscoasa# configure terminal
ciscoasa(config)# mode ?

configure mode commands/options:
  multiple   Multiple mode; mode with security contexts
  noconfirm  Do not prompt for confirmation
  single     Single mode; mode without security contexts
ciscoasa(config)# mode multiple
WARNING: This command will change the behavior of the device
WARNING: This command will initiate a Reboot
Proceed with change mode? [confirm]
Convert the system configuration? [confirm]
!
The old running configuration file will be written to flash

Converting the configuration - this may take several minutes for a large configuration

The admin context configuration will be written to flash

The new running configuration file was written to flash
Security context mode: multiple


***
*** --- SHUTDOWN NOW ---
***
*** Message to all terminals:
***
***   change mode
REBOOT: open message queue fail: No such file or directory/2
REBOOT: enforce reboot...
Restarting system.
machine restart

<OUTPUT TRUNCATED>


ciscoasa# configure terminal
ciscoasa(config)# interface gigabitethernet0   // WE UNSHUT MAIN INTERFACES IN SYSTEM CONTEXT
ciscoasa(config-if)# ?

Interface configuration commands:
  channel-group  Etherchannel/port bundling configuration
  default        Set a command to its defaults
  description    Interface specific description
  exit           Exit from interface configuration mode
  help           Interactive help for interface subcommands
  lacp           LACP interface subcommands
  no             Negate a command or set its defaults
  shutdown       Shutdown the selected interface
ciscoasa(config-if)# no shutdown
ciscoasa(config-if)# interface gigabitethernet1
ciscoasa(config-if)# no shutdown
ciscoasa(config-if)# exit
ciscoasa(config)# context ?

configure mode commands/options:
  WORD  Symbolic name of the context
ciscoasa(config)# context CONTEXT-A
Creating context 'CONTEXT-A'... Done. (2)

ciscoasa(config-ctx)# ?

Context configuration commands:
  allocate-interface   Allocate interface to context
  allocate-ips         Allocate IPS virtual sensor to context
  config-url           Configure URL for a context configuration
  description          Provide a description of the context
  exit                 Exit from context configuration mode
  help                 Interactive help for context subcommands
  join-failover-group  Join a context to a failover group
  member               Configure class membership for a context
  no                   Negate a command
ciscoasa(config-ctx)# allocate-interface ?

context mode commands/options:
  WORD  Indicate interfaces assigned to the context
ciscoasa(config-ctx)# allocate-interface gigabitethernet0 ?

context mode commands/options:
  WORD       Optional interface name mapping for the context
  invisible  Optional flag for hiding hardware property in context (default)
  visible    Optional flag for publishing hardware property in context
  <cr>
ciscoasa(config-ctx)# allocate-interface gigabitethernet0 intg0
ciscoasa(config-ctx)# allocate-interface gigabitethernet1 intg1
ciscoasa(config-ctx)# config-url ?

context mode commands/options:
  disk0:  A URL beginning with this prefix for the context's config (file need
          not exist)
  flash:  A URL beginning with this prefix for the context's config (file need
          not exist)
  ftp:    A URL beginning with this prefix for the context's config (file need
          not exist)
  http:   A URL beginning with this prefix for the context's config (file need
          not exist)
  https:  A URL beginning with this prefix for the context's config (file need
          not exist)
  smb:    A URL beginning with this prefix for the context's config (file need
          not exist)
  tftp:   A URL beginning with this prefix for the context's config (file need
          not exist)
ciscoasa(config-ctx)# config-url disk0:/CONTEXT-A.cfg
WARNING: Could not fetch the URL disk0:/CONTEXT-A.cfg
INFO: Creating context with default config
ciscoasa/CONTEXT-A(config)# interface intg0
ciscoasa/CONTEXT-A(config-if)# ip address 192.168.1.1 255.255.255.0
ciscoasa/CONTEXT-A(config-if)# no shutdown
ciscoasa/CONTEXT-A(config-if)# nameif inside
INFO: Security level for "inside" set to 100 by default.
ciscoasa/CONTEXT-A(config-if)# interface intg1
ciscoasa/CONTEXT-A(config-if)# ip address 209.165.200.1 255.255.255.0
ciscoasa/CONTEXT-A(config-if)# no shutdown
ciscoasa/CONTEXT-A(config-if)# nameif outside
INFO: Security level for "outside" set to 0 by default.
ciscoasa(config-ctx)# exit
ciscoasa(config)# context CONTEXT-B
Creating context 'CONTEXT-B'... Done. (3)
ciscoasa(config-ctx)# allocate-interface gigabitethernet0 intg0
ciscoasa(config-ctx)# allocate-interface gigabitethernet1 intg1

ciscoasa/CONTEXT-B(config)# interface intg0
ciscoasa/CONTEXT-B(config-if)# ip address 172.16.1.1 255.255.255.0
ciscoasa/CONTEXT-B(config-if)# no shutdown
ciscoasa/CONTEXT-B(config-if)# nameif inside
INFO: Security level for "inside" set to 100 by default.
ciscoasa/CONTEXT-B(config-if)# interface intg1
ciscoasa/CONTEXT-B(config-if)# ip address 209.165.200.1 255.255.255.0
ERROR: This address conflicts with another address on net
ciscoasa/CONTEXT-B(config-if)# ip address 209.165.200.2 255.255.255.0
ciscoasa/CONTEXT-B(config-if)# no shutdown
ciscoasa/CONTEXT-B(config-if)# nameif outside
INFO: Security level for "outside" set to 0 by default.
ciscoasa(config-ctx)# config-url disk0:/CONTEXT-B.cfg
WARNING: Could not fetch the URL disk0:/CONTEXT-B.cfg
INFO: Creating context with default config
ciscoasa(config-ctx)# exit
ciscoasa(config)# admin-context ?

configure mode commands/options:
  WORD  Name of administrative context
ciscoasa(config)# admin-context admin   // ASSIGN ADMIN CONTEXT AS "ADMIN" FOR REMOTE MANAGEMENT
ciscoasa(config)# context admin
ciscoasa(config-ctx)# config-url disk0:/admin.cfg

Cryptochecksum (changed): d9951253 3b82d2ce 840166f8 ccd3d7f1
INFO: Context admin was created with URL disk0:/admin.cfg
INFO: Admin context will take some time to come up .... please wait.
ciscoasa(config-ctx)# allocate-interface gigabitethernet0 intg0
ciscoasa(config-ctx)# allocate-interface gigabitethernet1 intg1
ciscoasa(config-ctx)# end
ciscoasa# changeto ?

  context  Change to context
  system   Change to system space
ciscoasa# changeto context ?

  WORD  Context name
ciscoasa# changeto context admin
ciscoasa/admin# configure terminal
ciscoasa/admin(config)# interface intg0
ciscoasa/admin(config-if)# ip address 10.1.1.1 255.255.255.0
ciscoasa/admin(config-if)# no shutdown
ciscoasa/admin(config-if)# nameif inside
INFO: Security level for "inside" set to 100 by default.
ciscoasa/admin(config-if)# exit
ciscoasa/admin(config)# http server enable
ciscoasa/admin(config)# http 0 0 inside  // HTTPS/ASDM ACCESS FROM ANY IP SOURCE COMING FROM THE INSIDE INTERFACE
ciscoasa/admin(config)#end


Saturday, October 12, 2013

Configuring Access Control List (ACL) on an ASA

The access control list (ACL) is the very heart of every ASA device. The ASA provides an administrator with a full-featured set of access control methods, allowing access between network segments to be tightly controlled.

You can configure an interface access rules in the CLI by using the access-list command. ACLs are made up of one or more access control entries (ACE), each represented by one line in the ACL, that specifying a permit or deny rule, or remark.

ciscoasa(config)# access-list ?

configure mode commands/options:
  WORD < 241 char  Access list identifier
  alert-interval   Specify the alert interval for generating syslog message
                   106001 which alerts that the system has reached a deny flow
                   maximum. If not specified, the default value is 300 sec
  deny-flow-max    Specify the maximum number of concurrent deny flows that can
                   be created. If not specified, the default value is 4096
ciscoasa(config)# access-list INSIDE-IN ?

configure mode commands/options:
  deny      Specify packets to reject
  extended  Configure access policy for IP traffic through the system
  line      Use this to specify line number at which ACE should be entered
  permit    Specify packets to forward
  remark    Specify a comment (remark) for the access-list after this keyword
  rename    rename an existing access-list
  standard  Use this to configure policy having destination host or network
            only
  webtype   Use this to configure WebVPN related policy
ciscoasa(config)# access-list INSIDE-IN line 1 ?

configure mode commands/options:
  deny      Specify packets to reject
  extended  Configure access policy for IP traffic through the system
  permit    Specify packets to forward
  remark    Specify a comment (remark) for the access-list after this keyword
ciscoasa(config)# access-list INSIDE-IN line 1 extended ?

configure mode commands/options:
  deny    Specify packets to reject
  permit  Specify packets to forward
ciscoasa(config)# access-list INSIDE-IN line 1 extended permit ?

configure mode commands/options:
  <0-255>       Enter protocol number (0 - 255)
  ah
  eigrp
  esp
  gre
  icmp
  icmp6
  igmp
  igrp
  ip
  ipinip
  ipsec
  nos
  object        Specify a service object after this keyword
  object-group  Specify a service or protocol object-group after this keyword
  ospf
  pcp
  pim
  pptp
  snp
  tcp
  udp
ciscoasa(config)# access-list INSIDE-IN line 1 extended permit tcp ?

configure mode commands/options:
  A.B.C.D            Source IP address
  any                Abbreviation for source address and mask of 0.0.0.0
                     0.0.0.0
  host               Use this keyword to configure source host
  interface          Use interface address as source address
  object             Keyword to enter source object name
  object-group       Network object-group for source address
  object-group-user  User object-group for source address
  user               User for source address [<domain_nickname>\]<user_name>
  user-group         User-group for source address
                     [<domain_nickname>\\]<user_group_name>
ciscoasa(config)# access-list INSIDE-IN line 1 extended permit tcp 10.0.0.0 ?

configure mode commands/options:
  A.B.C.D  Netmask for source IP address
ciscoasa(config)# access-list INSIDE-IN line 1 extended permit tcp 10.0.0.0 255.255.255.0 ?

configure mode commands/options:
  A.B.C.D       Destination IP address
  any           Abbreviation for destination address and mask of 0.0.0.0
                0.0.0.0
  eq            Port equal to operator
  gt            Port greater than operator
  host          Use this keyword to configure destination host
  interface     Use interface address as destination address
  lt            Port less than operator
  neq           Port not equal to operator
  object        Keyword to enter destination object name
  object-group  Optional service object-group name for source port or network
                object-group for destination address
  range         Port range operator
ciscoasa(config)# access-list INSIDE-IN line 1 extended permit tcp 10.0.0.0 255.255.255.0 any ?

configure mode commands/options:
  eq            Port equal to operator
  gt            Port greater than operator
  inactive      Keyword for disabling an ACL element
  log           Keyword for enabling log option on this ACL element
  lt            Port less than operator
  neq           Port not equal to operator
  object-group  Optional service object-group for destination port
  range         Port range operator
  time-range    Keyword for attaching time-range option to this ACL element
  <cr>
ciscoasa(config)# access-list INSIDE-IN line 1 extended permit tcp 10.0.0.0 255.255.255.0 any eq ?

configure mode commands/options:
  <1-65535>        Enter port number (1 - 65535)
  aol
  bgp
  chargen
  cifs
  citrix-ica
  cmd
  ctiqbe
  daytime
  discard
  domain
  echo
  exec
  finger
  ftp
  ftp-data
  gopher
  h323
  hostname
  http
  https
  ident
  imap4
ciscoasa(config)# access-list INSIDE-IN line 1 extended permit tcp 10.0.0.0 255.255.255.0 any eq http
ciscoasa(config)# access-list OUTSIDE-IN line 2 remark EXPLICIT DENY ALL RULE
ciscoasa(config)# access-list OUTSIDE-IN line 3 extended deny ip any any ?

configure mode commands/options:
  inactive    Keyword for disabling an ACL element
  log         Keyword for enabling log option on this ACL element
  time-range  Keyword for attaching time-range option to this ACL element
  <cr>
ciscoasa(config)# access-list OUTSIDE-IN line 3 extended deny ip any any log ?

configure mode commands/options:
  <0-7>          Enter syslog level (0 - 7)
  Default        Keyword for restoring default log behavior
  alerts         Immediate action needed           (severity=1)
  critical       Critical conditions               (severity=2)
  debugging      Debugging messages                (severity=7)
  disable        Disable log option on this ACL element, (no log at all)
  emergencies    System is unusable                (severity=0)
  errors         Error conditions                  (severity=3)
  inactive       Keyword for disabling an ACL element
  informational  Informational messages            (severity=6)
  interval       Configure log interval, default value is 300 sec
  notifications  Normal but significant conditions (severity=5)
  time-range     Keyword for attaching time-range option to this ACL element
  warnings       Warning conditions                (severity=4)
  <cr>
ciscoasa(config)# access-list OUTSIDE-IN line 3 extended deny ip any any log 4 ?

configure mode commands/options:
  inactive    Keyword for disabling an ACL element
  interval    Configure log interval, default value is 300 sec
  time-range  Keyword for attaching time-range option to this ACL element
  <cr>
ciscoasa(config)# access-list OUTSIDE-IN line 3 extended deny ip any any log 4 interval 300
ciscoasa(config)# object network TIME.NIST.GOV
ciscoasa(config-network-object)# host 192.43.244.18
ciscoasa(config-network-object)# exit
ciscoasa(config)# access-list GLOBAL-ACL line 1 extended permit udp any object TIME.NIST.GOV eq ntp log ?

configure mode commands/options:
  <0-7>          Enter syslog level (0 - 7)
  Default        Keyword for restoring default log behavior
  alerts         Immediate action needed           (severity=1)
  critical       Critical conditions               (severity=2)
  debugging      Debugging messages                (severity=7)
  disable        Disable log option on this ACL element, (no log at all)
  emergencies    System is unusable                (severity=0)
  errors         Error conditions                  (severity=3)
  inactive       Keyword for disabling an ACL element
  informational  Informational messages            (severity=6)
  interval       Configure log interval, default value is 300 sec
  notifications  Normal but significant conditions (severity=5)
  time-range     Keyword for attaching time-range option to this ACL element
  warnings       Warning conditions                (severity=4)
  <cr>
ciscoasa(config)# access-list GLOBAL-ACL line 1 extended permit udp any object TIME.NIST.GOV eq ntp log disable
ciscoasa(config)# access-group ?

configure mode commands/options:
  WORD  Specify the name of an access-list
ciscoasa(config)# access-group INSIDE-IN ?

configure mode commands/options:
  global  For traffic on all interfaces
  in      For input traffic
  out     For output traffic
  <cr>
ciscoasa(config)# access-group INSIDE-IN in ?

configure mode commands/options:
  interface  Keyword to specify an interface
ciscoasa(config)# access-group INSIDE-IN in interface ?

configure mode commands/options:
Current available interface(s):
  dmz      Name of interface GigabitEthernet1
  inside   Name of interface GigabitEthernet0
  outside  Name of interface GigabitEthernet2
ciscoasa(config)# access-group INSIDE-IN in interface inside
ciscoasa(config)# access-group OUTSIDE-IN in interface outside
ciscoasa(config)# access-group GLOBAL-ACL global


The ASDM Access Rules table contains several features that enable you to quickly and efficiently manage it.

From the menu, you can choose to add, insert, edit or delete an access rule. You can also easily copy (clone) a rule, for instance, when you add another web server. Just clone the existing web server rule, and then edit it to change the destination IP address.


You can change the order of rules, using either the cut/copy and paste options or the move up/down arrows. Remember that access rules are evaluated in order and positioning of the rule is critical to its functionality.


You can also clear the hit counter for a specific rule (right-click menu) or all access rules (button on the toolbar), which is commonly required during troubleshooting. You can also show log messages generated by a chosen rule (right-click menu) or by all access rules (button on the toolbar). Additionally from the right-click menu, you can export the contents of the Access Rules table to a comma-separated value (CSV) format file.

You can edit a rule in place (rather than opening the Edit Access Rule dialog box) and alter the contents within the Access Rules window. Rules can also be temporarily disabled and if you want to permanently remove a rule, simply delete it.

Saturday, October 5, 2013

New NAT Options in IOS Versions 8.3 and Later

* One significant change in NAT with software versions 8.3 and higher is that NAT control (enforcing use of NAT) is no longer a supported. 

* The implementation of NAT is done through the use of network objects (hence, "object-oriented")

* There is now an "any" option that can be used when defining ingress and egress interfaces in the NAT configuration.

* You can configure translations as part of network object definitions, which are added to configuration. This is known as "Auto NAT," which reduces complex configuration when only one translation policy is required for a host.

* You can configure a single NAT rule that will translate both the source and destination addresses in a packet. This is known as "Manual NAT" or "Twice NAT," because NAT can be performed twice - once on the source IP and the other on the destination IP.

* NAT rules can be defined as unidirectional, meaning only traffic sourced from a defined object can use the translation. Connections toward the object must match a different NAT rule, or they will not be translated.

In this scenario, we have two application servers on the DMZ interface that require access from the Internet. A web server with native (local) IP address 172.16.0.5 and an FTP server with native IP address 172.16.0.10. The web server will use translated (global) IP address 209.165.200.228 when communicating with the outside interface (the Internet), and the FTP server will use translated IP address 209.165.200.229. 


ciscoasa(config)# object ?

configure mode commands/options:
  network  Specifies a host, subnet or range IP addresses
  service  Specifies a protocol/port
ciscoasa(config)# object network ?

configure mode commands/options:
  WORD < 65 char  Specifies object ID (1-64 characters)
ciscoasa(config)# object network DMZ-FTP-PUB
ciscoasa(config-network-object)# ?

  description  Specify description text
  fqdn         Enter this keyword to specify an FQDN
  help         Help for network object configuration commands
  host         Enter this keyword to specify a single host object
  nat          Enable NAT on a singleton object
  no           Remove an object or description from object
  range        Enter this keyword to specify a range
  subnet       Enter this keyword to specify a subnet
ciscoasa(config-network-object)# host ?

network-object mode commands/options:
  A.B.C.D     Enter a host IP address
  X:X:X:X::X  Enter a host IPV6 address
ciscoasa(config-network-object)# host 209.165.200.229
ciscoasa(config-network-object)# exit
ciscoasa(config)# object network DMZ-FTP-PRIV
ciscoasa(config-network-object)# host 172.16.0.10
ciscoasa(config-network-object)# nat ?

network-object mode commands/options:
  (        Open parenthesis for (<real_if_name>,<mapped_if_name>) pair where
           <real_if_name> is the prenat interface and <mapped_if_name> is the
           postnat interface
  dynamic  Specify NAT type as dynamic
  static   Specify NAT type as static

configure mode commands/options:
  (               Open parenthesis for (<internal_if_name>,<external_if_name>)
                  pair where <internal_if_name> is the Internal or prenat
                  interface and <external_if_name> is the External or postnat
                  interface
  <1-2147483647>  Position of NAT rule within before auto section
  after-auto      Insert NAT rule after auto section
  source          Source NAT parameters
ciscoasa(config-network-object)# nat (?

network-object mode commands/options:
Current available interface(s):

  DMZ      Name of interface GigabitEthernet1
  any      Global address space
  inside   Name of interface GigabitEthernet0
  outside  Name of interface GigabitEthernet2

configure mode commands/options:
Current available interface(s):

  DMZ      Name of interface GigabitEthernet1
  any      Global address space
  inside   Name of interface GigabitEthernet0
  outside  Name of interface GigabitEthernet2
ciscoasa(config-network-object)# nat (DMZ,outside) ?

network-object mode commands/options:
  dynamic  Specify NAT type as dynamic
  static   Specify NAT type as static

configure mode commands/options:
  <1-2147483647>  Position of NAT rule within before auto section
  after-auto      Insert NAT rule after auto section
  source          Source NAT parameters
ciscoasa(config-network-object)# nat (DMZ,outside) static ?

network-object mode commands/options:
  A.B.C.D    Mapped IP address
  WORD       Mapped network object/object-group name
  interface  Use interface address as mapped IP
ciscoasa(config-network-object)# nat (DMZ,outside) static DMZ-FTP-PUB
ciscoasa(config-network-object)# exit
ciscoasa(config)# object network DMZ-WEB-PUB
ciscoasa(config-network-object)# host 209.165.200.228
ciscoasa(config-network-object)# exit
ciscoasa(config)# object network DMZ-WEB-PRIV
ciscoasa(config-network-object)# host 172.16.0.5
ciscoasa(config-network-object)# nat (DMZ,outside) static DMZ-WEB-PUB

Saturday, September 28, 2013

Configuring Dynamic Inside PAT on an ASA (pre-8.3)

There are four pieces of information necessary for an ASA to perform NAT:

* Original source IP address (and port) in the packet

* Interface where the original packet enters the ASA (ingress interface)

* Interface where the packet will exit the ASA (egress interface)

* Translated address (and, optionally, port) to insert into the packet

Dynamic inside PAT creates many-to-one translations, allowing several local (original) IP addresses to share a single global (translated) IP address. It does so by creating a temporary translation of both the original IP address and the original source port number to a global IP address and unique global port number, for each translated session. These translations are created and added to the translation table for each outbound TCP or UDP session requiring PAT. These are removed from the NAT table when the OSI Layer 4 session closes.

You can define an available IP address, or you can use of the ASA's IP address on the egress interface. Using the ASA interface IP is particularly usefeul in environments where you are provided with only one IP address (usually dynamic) by an ISP.

Dynamic PAT is typically used for client hosts that need outbound connectivity only, and when there are not enough global IP addresses available to assign a unique global address to each local host.


ASA802(config)# nat ?

configure mode commands/options:
  (  Open parenthesis for the name of the network interface where the
     hosts/network designated by the local IP address are accessed
ASA802(config)# nat (?

configure mode commands/options:
Current available interface(s):

  inside   Name of interface Ethernet0/1
  outside  Name of interface Ethernet0/0
ASA802(config)# nat (inside) ?

configure mode commands/options:
  <0-2147483647>  The <nat_id> of this group of hosts/networks. This <nat_id>
                  will be referenced by the global command to associate a
                  global pool with the local IP address. <nat_id> '0' is used
                  to indicate no address translation for local IP. The limit is
                  65535 with access-lists
ASA802(config)# nat (inside) 1 ?

configure mode commands/options:
  Hostname or A.B.C.D  The hosts/networks in this <nat_id> group, '0' indicates
                       all networks or the default <nat_id> group
  access-list          Specify access-list name after this keyword
ASA802(config)# nat (inside) 1 10.1.1.0 ?

configure mode commands/options:
  A.B.C.D  IP netmask to apply to the local IP address
  <cr>
ASA802(config)# nat (inside) 1 10.1.1.0 255.255.255.0 ?

configure mode commands/options:
  <0-65535>    The maximum number of simultaneous TCP connections the local IP
               hosts are to allow, default is 0 which means unlimited
               connections. Idle connections are closed after the time
               specified by the timeout conn command
  dns          Rewrite DNS address record
  norandomseq  Disable TCP sequence number randomization
  outside      Enable Outside NAT
  tcp          Configure TCP specific parameters
  udp          Configure UDP specific parameters
  <cr>
ASA802(config)# nat (inside) 1 10.1.1.0 255.255.255.0 tcp ?

configure mode commands/options:
  <0-65535>  The maximum number of simultaneous TCP connections the local IP
             hosts are to allow, default is 0 which means unlimited
             connections. Idle connections are closed after the time specified
             by the timeout conn command
ASA802(config)# nat (inside) 1 10.1.1.0 255.255.255.0 tcp 0 ?

configure mode commands/options:
  <0-65535>  The maximum number of embryonic connections per host, default is
             0, which means unlimited connections. An embryonic connection is a
             connection request that has not finished the necessary handshake
             between source and destination
  <cr>
ASA802(config)# nat (inside) 1 10.1.1.0 255.255.255.0 tcp 0 0 ?

configure mode commands/options:
  norandomseq  Disable TCP sequence number randomization
  udp          Configure UDP specific parameters
  <cr>
ASA802(config)# nat (inside) 1 10.1.1.0 255.255.255.0 tcp 0 0 udp ?

configure mode commands/options:
  <0-65535>  The maximum number of simultaneous UDP connections the local IP
             hosts are to allow, default is 0 which means unlimited
             connections. Idle connections are closed after the time specified
             by the timeout conn command
ASA802(config)# nat (inside) 1 10.1.1.0 255.255.255.0 tcp 0 0 udp 0
ASA802(config)# global ?

configure mode commands/options:
  (  Open parenthesis for the external network interface name
ASA802(config)# global (?

configure mode commands/options:
Current available interface(s):

  inside   Name of interface Ethernet0/1
  outside  Name of interface Ethernet0/0
ASA802(config)# global (outside) ?

configure mode commands/options:
  <0-2147483647>  The id of the NAT group that will draw from these global
                  addresses
ASA802(config)# global (outside) 1 ?

configure mode commands/options:
  WORD       Enter IP address or a range of IP addresses <start_ip>[-<end_ip>]
  interface  Specifies PAT using the IP address at the interface
ASA802(config)# global (outside) 1 interface

ASA802# show xlate
0 in use, 1 most used


My PC is still not able to ping the Internet (8.8.8.8) and there's no output on the NAT Table (0 in use). So I've manually created a policy (Modular Policy Framework or MPF) to allow ICMP or ping and applied it under the ASA's inside interface. I've also enabled the nat-control (disabled by default) to enforce packets from the inside interface to the outside interface to match a NAT rule.

policy-map inside-policy
 class inside-class
  inspect icmp
!
service-policy inside-policy interface inside  

ASA802(config)# nat?

configure mode commands/options:
  nat    nat-control
ASA802(config)# nat-control


ASA802# show xlate
2 in use, 2 most used
PAT Global 200.1.1.1(1024) Local 10.1.1.10(2985)
PAT Global 200.1.1.1(14) Local 10.1.1.10 ICMP id 1
ASA802# show xlate detail
2 in use, 2 most used
Flags: D - DNS, d - dump, I - identity, i - dynamic, n - no random,
       r - portmap, s - static
ICMP PAT from inside:10.1.1.10/1 to outside:200.1.1.1/15 flags ri
TCP PAT from inside:10.1.1.10/2985 to outside:200.1.1.1/1024 flags ri

Saturday, September 14, 2013

Configure Syslog and Debug Facility on an ASA

Most issues with remote management access appears in the ASA system logs (or to a remote syslog server). Use the show logging command or the ASDM real-time log viewer in order to examine the log files on the ASA.

ciscoasa(config)# logging ?

configure mode commands/options:
  asdm                      Set logging level or list for ASDM
  asdm-buffer-size          Specify ASDM logging buffer size
  buffer-size               Specify logging memory buffer size
  buffered                  Set buffer logging level or list
  class                     Specify logging event class
  console                   Set console logging level or list
  debug-trace               Enable logging of redirect debug-trace output to
                            syslog
  device-id                 Specify the device-id to be included in all
                            non-EMBLEM formatted syslog messages
  emblem                    Enable logging Emblem format on all output
                            supported destinations
  enable                    Enable logging to all output supported destinations
  facility                  Specify the syslog facility, the default is 20
  flash-bufferwrap          Save logging buffer to flash when buffer
                            wrap-around
  flash-maximum-allocation  Specify logging maximum flash space allocation
  flash-minimum-free        Specify logging minimum flash free space threshold
  flow-export-syslogs       Enable/Disable syslogs whose information is
                            captured by NetFlow
  from-address              Specify the from address for the mail logging
  ftp-bufferwrap            Save logging buffer using FTP when buffer
                            wrap-around
  ftp-server                Specify FTP server parameters
  history                   Set the SNMP message level or list for sending
                            syslog traps
  host                      Send syslog messages to a host
  list                      Specify logging event list
  mail                      Set mail logging level or list
  message                   Specify a message to be allowed
  monitor                   Specify that syslog messages appear on Telnet
                            sessions to the Firewall console
  permit-hostdown           Allow new connection even if TCP syslog server is
                            down
  queue                     Specify queue size for storing syslog messages,
                            default is 512, 0 means unlimited (subject to
                            available memory)
  rate-limit                Specify logging rate-limit parameters
  recipient-address         Specify the mail logging recipient address and
                            level
  standby                   Enable logging on standby unit with failover
                            enabled, warning: this option causes twice as much
                            traffic on the syslog server
  timestamp                 Enable logging timestamp on syslog messages
  trap                      Set logging level or list for syslog server

exec mode commands/options:
  savelog  Save logging buffer to flash

ciscoasa(config)# logging enable
ciscoasa(config)# logging buffered  ?

configure mode commands/options:
  <0-7>          Enter syslog level (0 - 7)
  WORD           Specify the name of logging list
  alerts         Immediate action needed           (severity=1)
  critical       Critical conditions               (severity=2)
  debugging      Debugging messages                (severity=7)
  emergencies    System is unusable                (severity=0)
  errors         Error conditions                  (severity=3)
  informational  Informational messages            (severity=6)
  notifications  Normal but significant conditions (severity=5)
  warnings       Warning conditions                (severity=4)
ciscoasa(config)# logging buffered debugging
ciscoasa(config)#
%ASA-5-111008: User 'enable_15' executed the 'logging buffered debugging' command.
%ASA-5-111010: User 'enable_15', running 'CLI' from IP 0.0.0.0, executed 'logging buffered debugging'
ciscoasa(config)# show logging
Syslog logging: enabled
    Facility: 20
    Timestamp logging: disabled
    Standby logging: disabled
    Debug-trace logging: disabled
    Console logging: disabled
    Monitor logging: disabled
    Buffer logging: level debugging, 2 messages logged
    Trap logging: disabled
    Permit-hostdown logging: disabled
    History logging: disabled
    Device ID: disabled
    Mail logging: disabled
    ASDM logging: disabled


If you wish to log all messages from all severity levels, it is strongly recommended that you do so to the internal buffer, and never to the console. In fact, it is generally recommended to leave console logging disabled.

The Cisco ASDM also contains a powerful event viewer that you can use to display a real-time messages from the ASA. This event viewer is particularly useful when you are troubleshooting ASA software and configuration issues, or when you are monitoring real-time activity over the ASA.

You enable logging to the internal ASDM event viewer by configuring the ASDM logging destination and specifying a logging filter, in the same manner as for other logging destinations.

ciscoasa(config)# logging asdm ?

configure mode commands/options:
  <0-7>          Enter syslog level (0 - 7)
  WORD           Specify the name of logging list
  alerts         Immediate action needed           (severity=1)
  critical       Critical conditions               (severity=2)
  debugging      Debugging messages                (severity=7)
  emergencies    System is unusable                (severity=0)
  errors         Error conditions                  (severity=3)
  informational  Informational messages            (severity=6)
  notifications  Normal but significant conditions (severity=5)
  warnings       Warning conditions                (severity=4)
ciscoasa(config)# logging asdm informational


If the syslog messages don't pinpoint the issue, consider debugging management protocols on the ASA, such as the following:

* debug ssh: Debugs the SSH daemons to determine low-level protocol failures, such as algorithm or version incompatibility.

* debug http: Debugs HTTP exchanges to determine problems with the ASDM image.

* debug snmp: Debugs SNMP exchanges to help determine problems with SNMP authentication and OIDs.

ciscoasa# debug ssh ?

  <1-255>  Specify an optional debug level (default is 1)
  <cr>
ciscoasa# debug ssh
debug ssh  enabled at level 1
%ASA-5-111008: User 'enable_15' executed the 'debug ssh' command.
ciscoasa#
%ASA-6-302013: Built inbound TCP connection 1304 for management:10.1.1.10/3919 (10.1.1.10/3919) to identity:10.1.1.1/22 (10.1.1.1/22)
%ASA-3-315004: Fail to establish SSH session because RSA host key retrieval failed.
%ASA-6-315011: SSH session from 10.1.1.10 on interface management for user "" disconnected by SSH server, reason: "Internal error" (0x00)
Device ssh opened successfully.
SSH0: SSH client: IP = '10.1.1.10'  interface # = 2
SSH: unable to retrieve default host public key.  Please create a defauth RSA key pair before using SSH
SSH0: Session disconnected by SSH server - error 0x00 "Internal error"
%ASA-6-302014: Teardown TCP connection 1304 for management:10.1.1.10/3919 to identity:10.1.1.1/22 duration 0:00:00 bytes 0 TCP FINs

ciscoasa# debug http
debug http enabled at level 1.
ciscoasa# %ASA-5-111008: User 'enable_15' executed the 'debug http' command.
%ASA-5-111010: User 'enable_15', running 'CLI' from IP 0.0.0.0, executed 'debug http'
ciscoasa#
%ASA-3-710003: TCP access denied by ACL from 10.1.1.10/3966 to management:10.1.1.1/443
%ASA-7-710005: TCP request discarded from 10.1.1.10/3966 to management:10.1.1.1/443
%ASA-3-710003: TCP access denied by ACL from 10.1.1.10/3966 to management:10.1.1.1/443
%ASA-7-710005: TCP request discarded from 10.1.1.10/3966 to management:10.1.1.1/443


Finally, you can also troubleshoot possible issues between an ASA and a remote AAA server by using the debug tacacs or debug radius commands. You can specify conditional debugging (such as limiting to a single username) to avoid excessive output and performance issues.

ciscoasa# debug aaa ?

  accounting
  authentication
  authorization
  common
  internal
  shim
  <cr>
ciscoasa# debug aaa authentication
debug aaa authentication enabled at level 1
ciscoasa# %ASA-5-111008: User 'enable_15' executed the 'debug aaa authentication' command.
ciscoasa# exit

Logoff

Username: %ASA-5-611103: User logged out: Uname: enable_15

Username: cisco
Password: *****
%ASA-6-113015: AAA user authentication Rejected : reason = Invalid password : local database : user = cisco
%ASA-6-611102: User authentication failed: Uname: cisco
%ASA-6-605004: Login denied from serial to console for user "cisco"
Username: John
Password: *****
%ASA-6-113012: AAA user authentication Successful : local database : user = John
%ASA-6-113008: AAA transaction status ACCEPT : user = John
Type help or '?' for a list of available commands.
%ASA-6-611101: User authentication succeeded: Uname: John
%ASA-6-605005: Login permitted from serial to console for user "John"
ciscoasa> enable
Password: 
ciscoasa# %ASA-5-502103: User priv level changed: Uname: enable_15 From: 1 To: 15

Sunday, September 1, 2013

Configuring AAA Access Using Remote AAA Server (TACACS+)

Configuring the use of  AAA authentication on the ASA is a three-step process::

Step 1: Create a AAA server group, if none already exists, and configure how servers in the group are accessed (protocol, port, and how to determine if a server is failing communication).

Step 2: Populate the server group with member servers. Define the location of each server and assign a symmetric password, which will be used to encrypt the communication session (or portions thereof, depending on the protocol used) between the ASA and the remote AAA server. This same password must be configured on the server when defining the ASA as a AAA client.

Step 3: Enable user authentication for each remote management access channel (the consoles). Define which authentication server group will be used for each console upon which AAA authentication is enabled (note that you define a group here, not a specific server).

For this scenario, we configured the ASA to authenticate the login info of the user "John" via TACACS+ protocol to the ACS (Access Control Server) before providing access to the firewall.

FIREWALL(config)# aaa authentication ?

configure mode commands/options:
  enable              Enable
  exclude             Exclude the service, local and foreign network which
                      needs to be authenticated, authorized, and accounted
  http                HTTP
  include             Include the service, local and foreign network which
                      needs to be authenticated, authorized, and accounted
  listener            Configure an HTTP or HTTPS authentication listener
  match               Specify this keyword to configure an ACL to match
  secure-http-client  Specify this keyword to ensure HTTP client authentication
                      is secured (over SSL)
  serial              Serial
  ssh                 SSH
  telnet              Telnet
FIREWALL(config)# aaa authentication enable ?

configure mode commands/options:
  console  Specify this keyword to identify a server group for administrative
           authentication
FIREWALL(config)# aaa authentication enable console ?

configure mode commands/options:
  LOCAL  Predefined server tag for AAA protocol 'local'
  WORD   Name of RADIUS or TACACS+ aaa-server group for administrative
         authentication
FIREWALL(config)# aaa authentication enable console TEST-TACACS
FIREWALL(config)# aaa-server ?

configure mode commands/options:
  WORD < 17 char  Enter a AAA server group tag

exec mode commands/options:
  WORD < 17 char  Enter a AAA server group tag
FIREWALL(config)# aaa-server TEST-TACACS ?

configure mode commands/options:
  (                    Open parenthesis for the name of the network interface
                       where the designated AAA server is accessed
  deadtime             Specify the amount of time that will elapse between the
                       disabling of the last server in the group and the
                       subsequent re-enabling of all servers
  host                 Enter this keyword to specify the IP address for the
                       server
  max-failed-attempts  Specify the maximum number of failures that will be
                       allowed for any server in the group before that server
                       is deactivated
  protocol             Enter the protocol for a AAA server group

exec mode commands/options:
  active  transition a FAILED AAA server to ACTIVE
  fail    transition an ACTIVE AAA server to FAILED
FIREWALL(config)# aaa-server TEST-TACACS protocol ?

configure mode commands/options:
  http-form  Protocol HTTP form-based
  kerberos   Protocol Kerberos
  ldap       Protocol LDAP
  nt         Protocol NT
  radius     Protocol RADIUS
  sdi        Protocol SDI
  tacacs+    Protocol TACACS+
FIREWALL(config)# aaa-server TEST-TACACS protocol tacacs+
FIREWALL(config-aaa-server-group)# ?

AAA server configuration commands:
  accounting-mode      Enter this keyword to specify accounting mode
  exit                 Exit from aaa-server group configuration mode
  help                 Help for AAA server configuration commands
  max-failed-attempts  Specify the maximum number of failures that will be
                       allowed for any server in the group before that server
                       is deactivated
  no                   Remove an item from aaa-server group configuration
  reactivation-mode    Specify the method by which failed servers are
                       reactivated
FIREWALL(config-aaa-server-group)# max-failed-attempts ?

aaa-server-group mode commands/options:
  <1-5>  Maximum number of failures (1-5)
FIREWALL(config-aaa-server-group)# max-failed-attempts 3
FIREWALL(config-aaa-server-group)# exit
FIREWALL(config)# aaa-server TEST-TACACS (inside) ?

configure mode commands/options:
  host  Enter this keyword to specify the IP address for the server
FIREWALL(config)# aaa-server TEST-TACACS (inside) host 10.1.1.20 ?

configure mode commands/options:
  WORD     Alphanumeric keyword up to 128 characters used as the encryption key
           for communicating with the AAA server.
  timeout  Specify the maximum time to wait for response from configured server
  <cr>
FIREWALL(config)# aaa-server TEST-TACACS (inside) host 10.1.1.20 cisco123
FIREWALL(config)# test ?

exec mode commands/options:
  aaa-server                    Test aaa-server configuration
  dynamic-access-policy-record  Test DAP posture assesment.
  regex                         Test a regular expression
  sso-server                    Test sso-server configuration
FIREWALL(config)# test aaa-server ?

exec mode commands/options:
  ad-agent        Test connectivity to the AD agent server
  authentication  Test connectivity to the authentication server
  authorization   Test connectivity to the authorization server
FIREWALL(config)# test aaa-server authentication ?

exec mode commands/options:
  WORD < 17 char  Enter a AAA server group tag
FIREWALL(config)# test aaa-server authentication TEST-TACACS ?

exec mode commands/options:
  delegate     Test Kerberos constrained delegation
  host         Enter this keyword to specify the IP address for the server
  impersonate  Test Kerberos protocol transition
  password     Password keyword
  self         Test Kerberos self-ticket retrieval
  username     Username keyword
  <cr>
FIREWALL(config)# test aaa-server authentication TEST-TACACS username ?

exec mode commands/options:
  WORD  Enter the username
FIREWALL(config)# test aaa-server authentication TEST-TACACS username John ?

exec mode commands/options:
  delegate     Test Kerberos constrained delegation
  impersonate  Test Kerberos protocol transition
  password     Password keyword
  <cr>
FIREWALL(config)# test aaa-server authentication TEST-TACACS username John password cisco123
Server IP Address or name: 10.1.1.20
INFO: Attempting Authentication test to IP address <10.1.1.20> (timeout: 12 seconds)
INFO: Authentication Successful
FIREWALL(config)# show aaa-server TEST-TACACS
Server Group:    TEST-TACACS
Server Protocol: tacacs+
Server Address:  10.1.1.20
Server port:     49
Server status:   ACTIVE, Last transaction at 17:56:06 UTC Mon Jul 1 2013
Number of pending requests              0
Average round trip time                 18ms
Number of authentication requests       27
Number of authorization requests        0
Number of accounting requests           0
Number of retransmissions               0
Number of accepts                       3
Number of rejects                       24
Number of challenges                    0
Number of malformed responses           0
Number of bad authenticators            0
Number of timeouts                      0
Number of unrecognized responses        0


Below are the configuration screenshots for the ACS/TACACS+ server: